AI TRUST CENTRE

AI governance you can put in front of your privacy team.

AI governance at Simply Stakeholders: how our stakeholder management software uses responsible AI, where your data goes, and who’s accountable. Written for the people who have to sign off. Certified to SOC 2 Type II and ISO/IEC 27001 · All AI processed in-region on Microsoft Azure and AWS · Your data never trains AI models
AI-trust-commitments-v2-green
Our commitments

Responsible AI: five commitments we make

Responsible AI starts with clear rules about your data. These commitments apply to every AI feature in Simply Stakeholders, from enrichment to Stakeholder AI Insights & Reports.

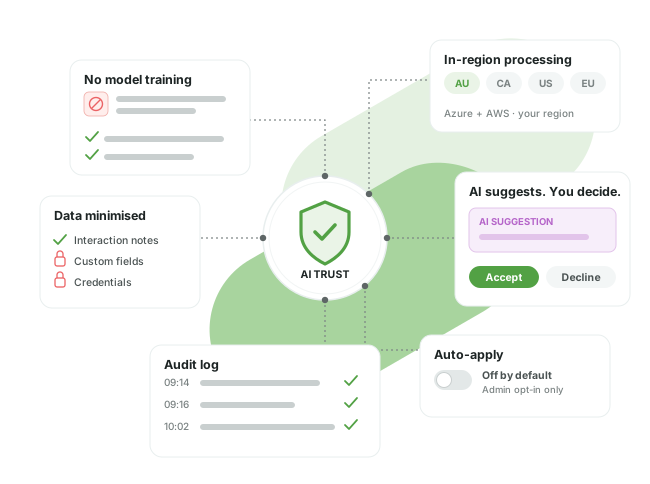
  1. Your data never trains AI models. Not ours, not Microsoft’s, not OpenAI’s, not Anthropic’s. This is contractually enforced.
  2. AI suggests, people decide. Nothing is auto-applied unless your own administrators switch it on.
  3. We send the minimum. Only interaction content is processed. Structured stakeholder fields, credentials and financial data are never sent to an AI model.
  4. In-region by default. All AI processing, including enrichment and reports, runs inside your region on Microsoft Azure and Amazon Web Services (AWS): Australia, Canada, the US or the EU.
  5. Every AI action is logged. Each AI call is audit-logged with the feature, timestamp and request type.
AI governance and data privacy controls in the Simply Stakeholders AI Trust Centre
Governance

AI governance: clear accountability for every AI feature

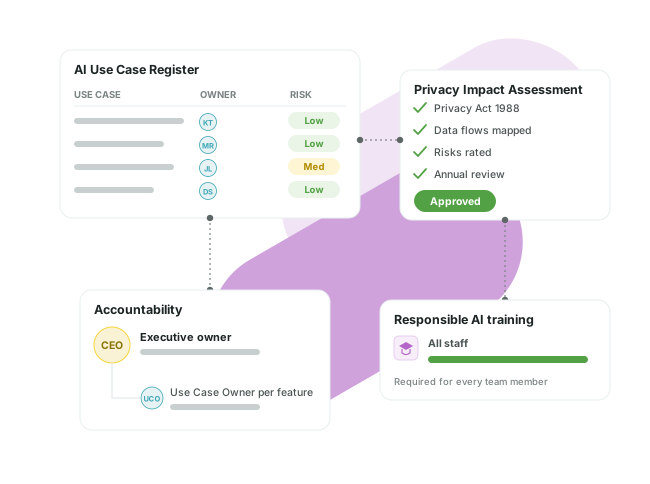
Our framework puts accountability for AI with our CEO. Every AI feature has a named Use Case Owner and is recorded in our AI Use Case Register with a risk rating. Each feature goes through a Privacy Impact Assessment against the Australian Privacy Act 1988 before release, reviewed at least annually. All staff complete Responsible AI training.

AI-trust-procurement-pack-aqua
For your procurement pack

AI data privacy: everything your reviewers will ask for

Procurement, privacy and IT teams can review our controls with these documents.

  • AI Policy, covering our AI providers, data handling and governance
  • Full AI Policy & Approach, available on request
  • Security and compliance documentation, including SOC 2 Type II and ISO/IEC 27001, available on request
  • Completed AI and security questionnaires for your procurement process, available on request

Contact us to request any of these documents.

AI governance and AI data privacy: the questions procurement asks

Which AI providers do you use?

We use enterprise AI services from Microsoft Azure (including Azure OpenAI Service and Azure AI Language) and Amazon Web Services (AWS). We don’t use consumer-grade AI endpoints.

Where is our data processed?

All AI processing, including enrichment and Insights & Reports, runs within your region on Microsoft Azure and AWS: Australia, Canada, the US or the EU.

Is our data used to train AI models?

No. This is contractually enforced through our agreements with our AI providers, including Microsoft’s Data Processing Addendum.

How long does the AI provider keep our data?

Microsoft retains processed content for a maximum of 48 hours for abuse monitoring, then permanently deletes it. Data sent for Insights & Reports is not retained by the AI provider beyond what is needed to generate the report.

What is sent to AI?

Interaction content, the names of people and organisations linked to it, addresses in the content, and email domains (never full email addresses). Headers, signatures, footers and URLs are stripped first.

What is never sent to AI?

Structured stakeholder fields (demographic, custom and relationship fields), passwords or credentials, and financial data.

Can we turn AI off?

Yes, field by field. Admins choose no AI, suggestions a person approves, or auto-apply with confirm and undo. Auto-apply is never on by default.

How do the Claude and Copilot connectors work?

Our MCP connector lets users ask questions of the stakeholder record and add to it, for example logging an interaction, from Claude or Microsoft Copilot. Access follows each user’s existing Simply Stakeholders permissions.

Can we see who used AI and how much?

Yes. Admins can see AI usage by user or project under Admin Settings.

What certifications do you hold?

Simply Stakeholders is certified to SOC 2 Type II and ISO/IEC 27001. Microsoft Azure also holds an IRAP assessment.

What AI governance framework does Simply Stakeholders follow?

Our framework sets accountability for AI at CEO level, assigns a named Use Case Owner to every AI feature, and records each one in an AI Use Case Register with a risk rating. Every feature passes a Privacy Impact Assessment against the Australian Privacy Act 1988 before release, every AI call is audit-logged, and all staff complete Responsible AI training.